
For CIOs, IT directors & procurement
Pass procurement on the first call.
The procurement checklist the unapproved card apps in your org fail on every line. SOC 2-aligned controls, GDPR-clean data handling, and contracts your legal team can sign without redlines.
Why InfoSec keeps blocking this
Three reasons every digital-card platform fails procurement.
01
Unapproved apps today.
Right now, your sales team is using a consumer-grade card app from the App Store - no SSO, no audit log, no DPA, no idea where the data lives. InfoSec finds out at the worst possible moment.
02
Offboard = unbounded risk.
VP of Sales leaves Friday. Her wallet pass with the company logo and 'VP, Acme' stays in 800 prospect phones until the heat death of the universe. There is no revoke button on a paper or consumer-grade card.
03
Brand walks out as 5,000 versions.
5,000 employees, 5,000 different cards, 5,000 different shades of 'the brand.' Your $5M rebrand is invisible because there's no enforcement layer between brand guidelines and what reps actually print.
A procurement-ready platform
Built to pass the security review on the first call.
SSO + SCIM = enforced identity. (coming soon) Google and Microsoft SSO are next on the roadmap; SAML and SCIM follow. Auto-provision on hire date, auto-revoke on departure date. Zero employees with active cards 90 days after they leave - by construction. Today, CSV bulk import and 30-second deactivation cover the same lifecycle.
Custom domain + brand-locked template. Cards live on cards.yourcompany.com, not heydrop.app. Brand template enforced at the org level - colors, fonts, logo, layout, mandatory fields. The 5,000-employee brand audit becomes a checkbox.
Audit log + DPA + subprocessors list. (coming soon) DPA with EU SCCs at /security/dpa. Subprocessors list at /security/subprocessors. Encryption in transit and at rest, scoped OAuth (we hold tokens, not passwords). Account activity reports on request today; the full exportable audit log ships with the enterprise security release. The artefacts your InfoSec team asks for are already published.
Enterprise capabilities
What's actually included on Enterprise plans.
The features procurement asks for and the features that actually matter once you're live.
SSO + SCIM (coming soon)
Google + Microsoft SSO next on the roadmap, SAML + SCIM 2.0 to follow. Auto-provision and auto-revoke against your IdP.
Custom domain
cards.yourcompany.com - SSL provisioned, traffic routed, brand intact end-to-end.
Exportable audit log (coming soon)
Every admin action timestamped. CSV export for InfoSec. Retention configurable per contract.
GDPR-clean by design
GDPR-clean data handling, encryption in transit and at rest, scoped OAuth, full data-subject controls.
Dedicated CSM + QBRs (coming soon)
Named CSM, white-glove onboarding, quarterly business reviews, direct escalation channel.
Brand-locked at scale
Brand template enforced across 5,000+ seats. Multiple templates per group. No drift, ever.
What changes for the org
From contract signature to next year's audit.
Quarter 1
Pilot to 500 seats, brand-locked.
SSO (coming soon) connected, custom domain provisioned, brand template approved, pilot rolled out to one division. CSM runs onboarding sessions for admins.
Quarter 2
5,000 seats live. Unapproved card apps retired.
Full org rollout. The five consumer-grade card apps your reps were using get retired in the IDP. One platform, one audit trail (coming soon), one billing line.
Year 1
Audit closes early.
Auditor asks for the offboarding log. Export takes 30 seconds. Asks for the brand-template versioning. Available in the admin panel. The card platform is no longer a security exception waiting to happen.
100-10k
Seats per deployment
GDPR
Infrastructure + data residency
Custom
Domain + branding end-to-end
Named CSM
Plus quarterly business reviews
Used by enterprise teams
Procurement-ready, security-reviewed, ops-loved.
Field, sales, marketing and people teams across the UK, US and GCC putting HeyDrop into production at enterprise scale.
Tech & Startups
“As a niche startup, we need to stand out at networking events and conferences. The digital cards sparked conversations about our tech-forward solutions, tripled our leads saved, and helped us make a memorable impression on investors and partners. It's exactly what we needed to showcase our innovation.”

Sales
“Since adding HeyDrop QR codes to our badges, we can instantly share contact details during visits. This has led to a 300% increase in follow-ups. Prospects save our information directly to their phones, ensuring our team is no longer perceived as anonymous callers.”

Mobile Workforce
“Reducing missed appointments for our mobile installers was a challenge. Now, customers receive installers' business cards in advance, allowing them to know who's coming and easily reschedule if needed. This has significantly improved customer trust and doubled our successful installations.”

HR & Admins
“Managing business cards for our growing workforce used to be a time-consuming and costly process. With HeyDrop, onboarding new team members is now instant, and we can make global updates in seconds - saving thousands on reprinting costs and manual labour.”

Platform
All-in-one networking platform
Built for IT to deploy, RevOps to measure, and every employee to use.
For your company
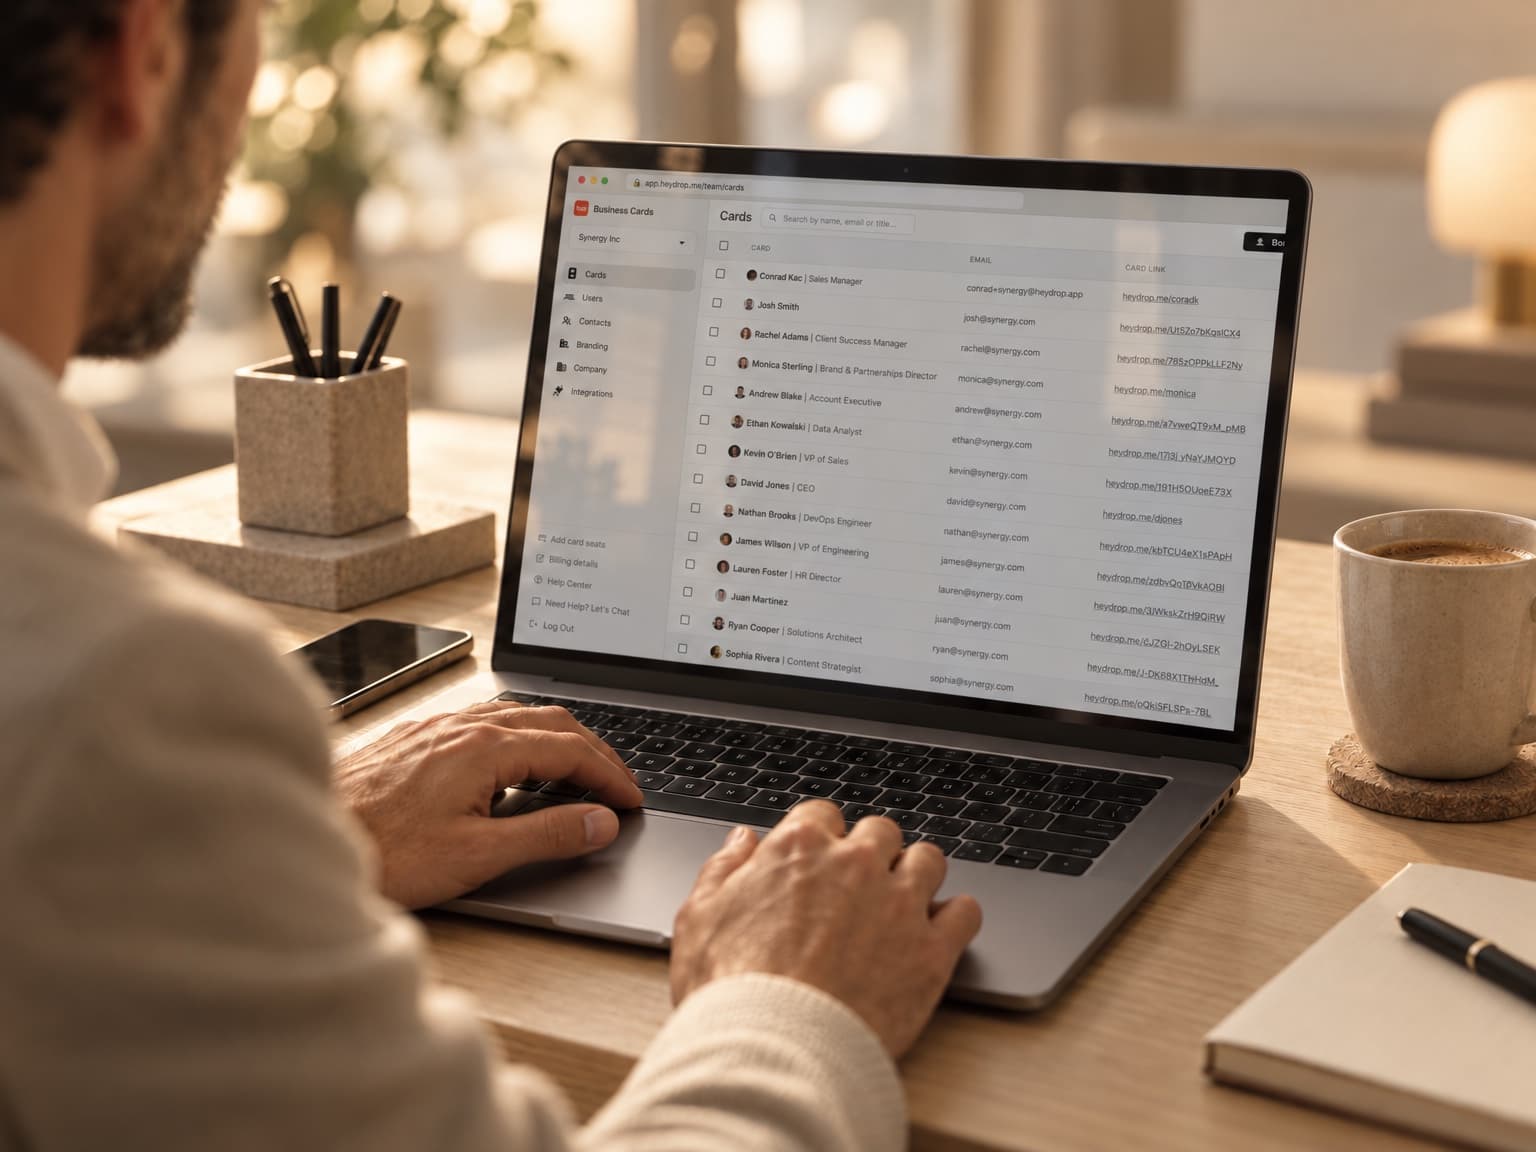
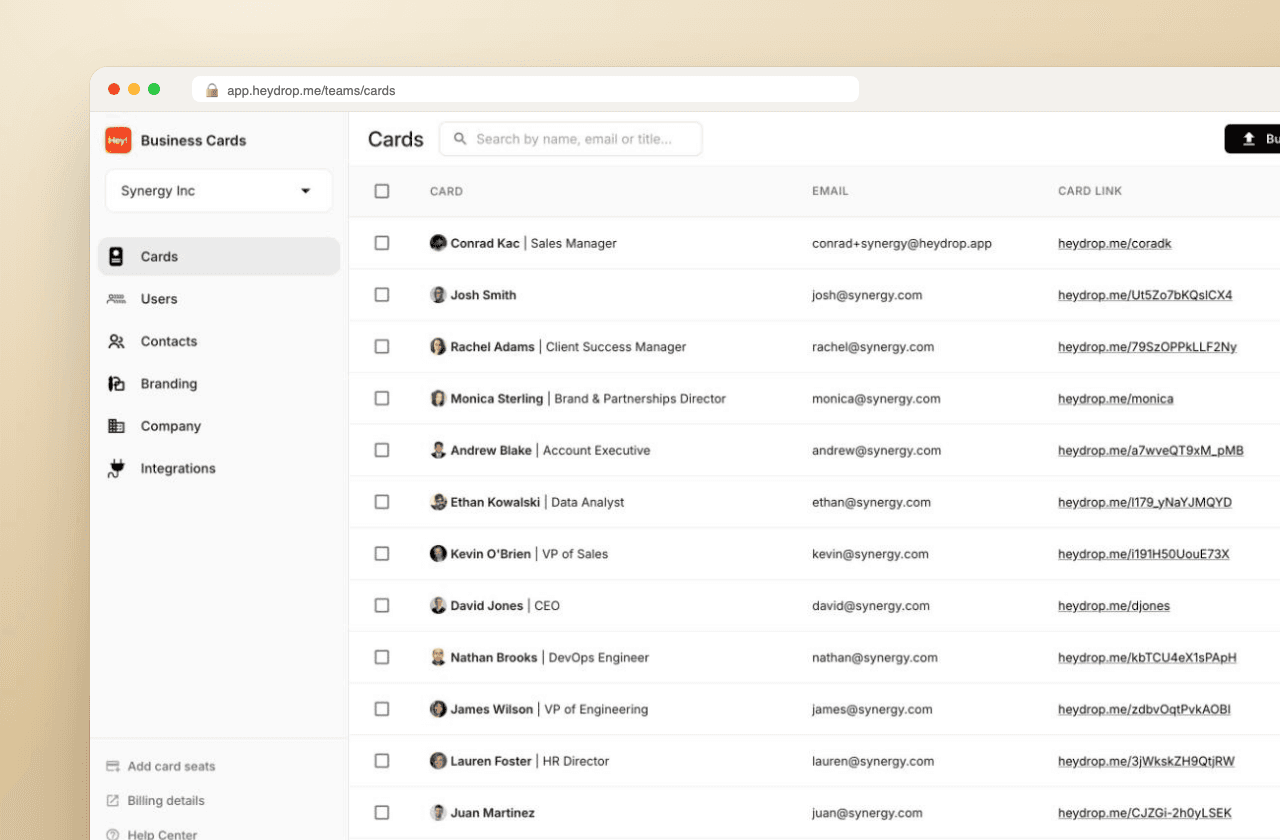
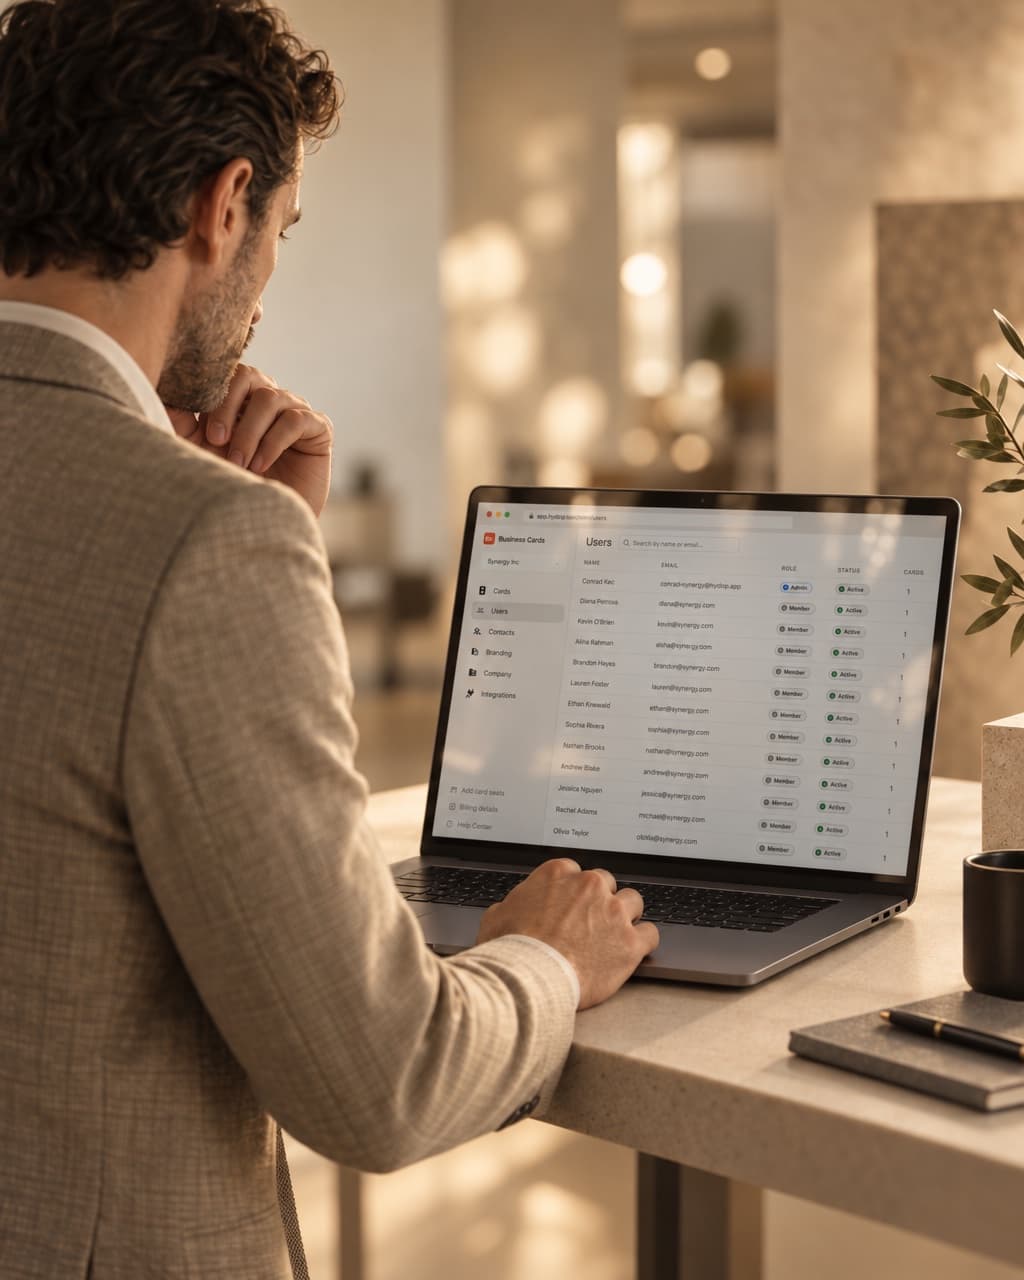
Web admin panel for card management, brand control and performance tracking across the org. Custom domains and dedicated CSM (coming soon) on Enterprise.
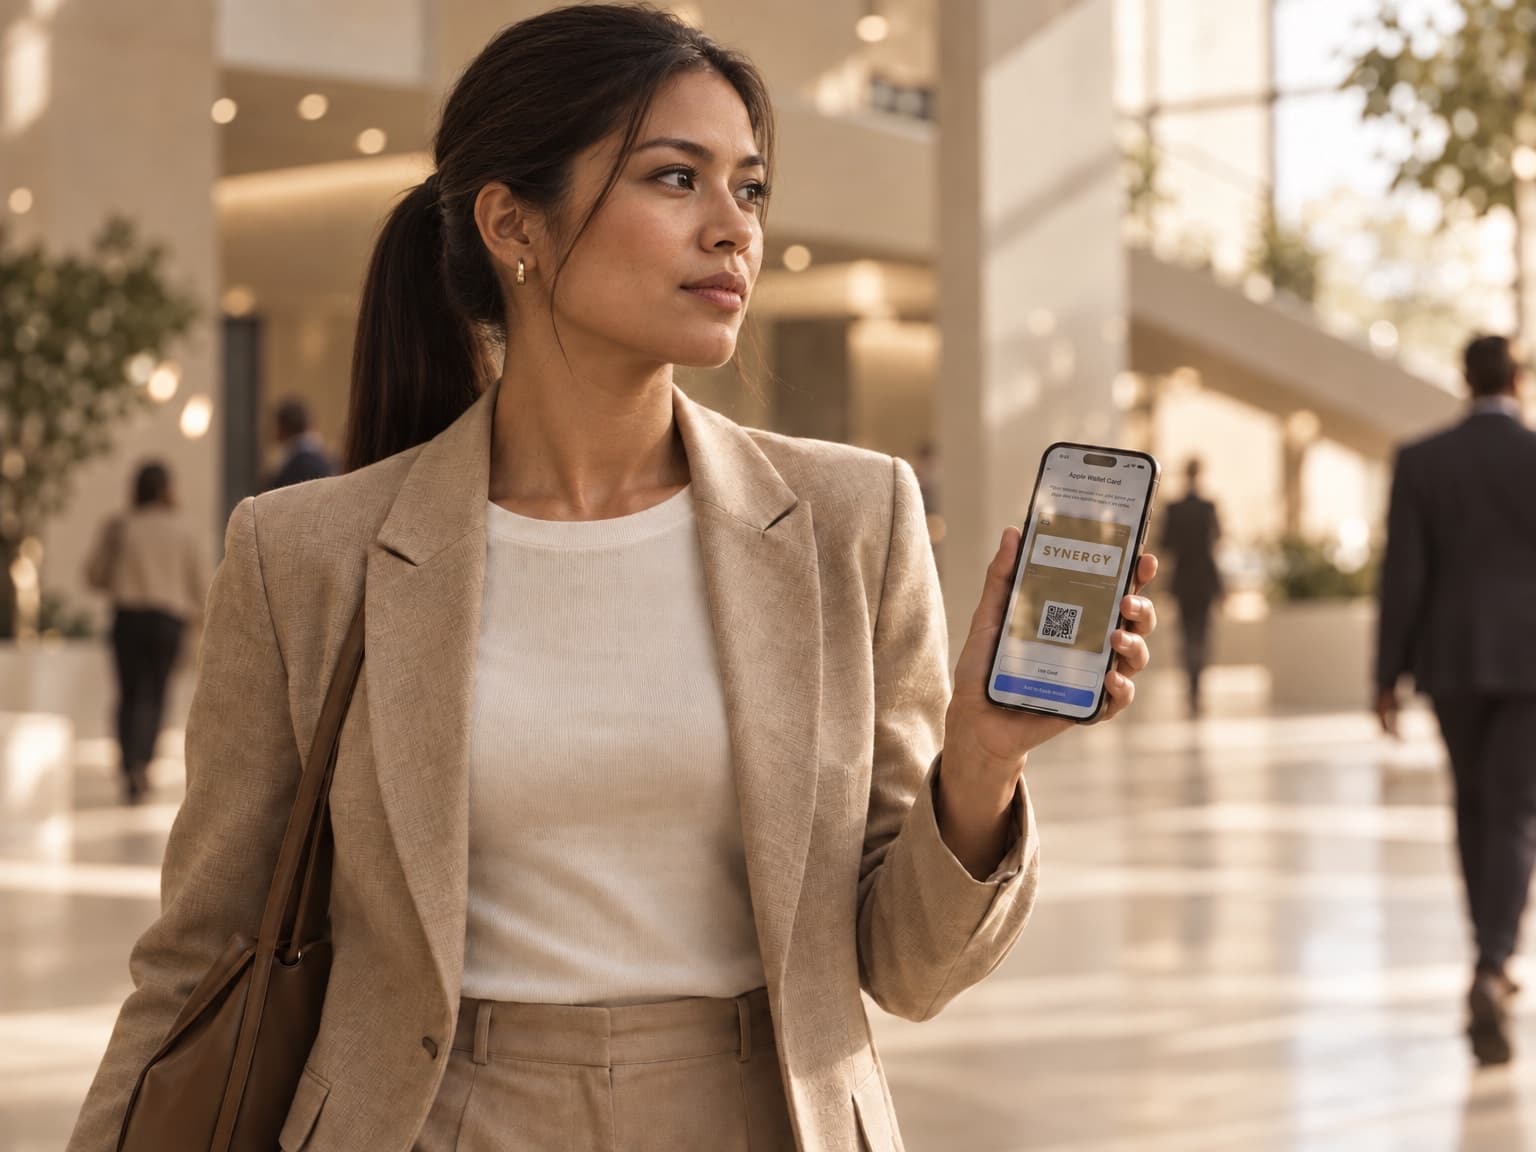
For your employees
QR code, Apple/Google Wallet card and mobile app to share, scan and push contacts straight to the CRM.
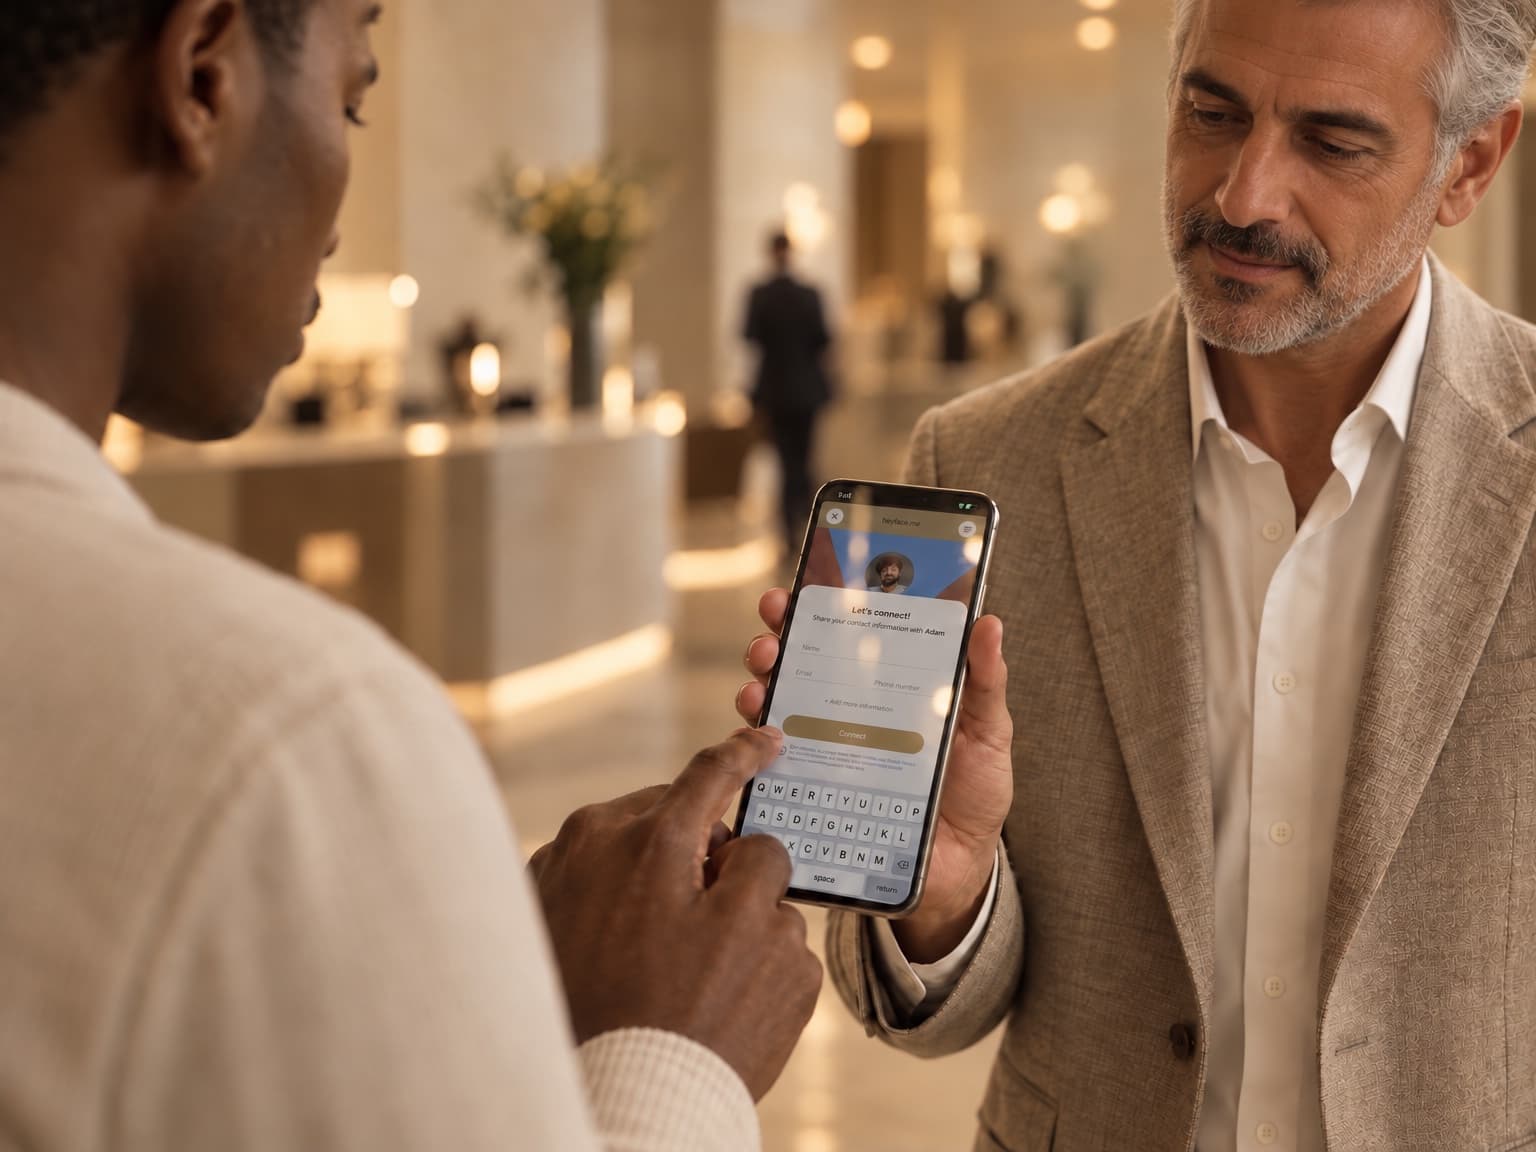
For your clients
Branded micro-websites that make it easy to exchange contacts and stay connected with your business.
A real procurement timeline
From security review to org-wide live.
Week 1-4
Security review: Trust Center, security questionnaire under NDA, DPA + EU SCCs reviewed by legal, subprocessors list logged. Pen-test summary on request. Most reviews close inside 4 weeks.
Week 5-8
Contract finalized. CSM kicks off rollout - SSO (coming soon) config, custom domain SSL provisioned, brand template + multi-template architecture approved by Marketing. Pilot division onboarded.
Week 9-16
Org-wide rollout. Five-thousand seats live in waves by division. Shadow-IT card apps decommissioned in IdP. Quarterly review scheduled. Pipeline-from-events attribution ships in HubSpot.
The artefacts InfoSec asks for
Already published.
Trust Center at /security. DPA at /security/dpa with EU SCCs. Subprocessors list at /security/subprocessors. Privacy policy, security practices, data deletion procedures all live. Security questionnaire shared under NDA on request. Open the Trust Center.
- Custom domain provisioning included on Enterprise plans.
- Multiple brand templates per division - Sales vs. Field vs. Executives.
- Audit log (coming soon) exportable to CSV - InfoSec gets a real artefact, not a screenshot.
Procurement-ready
Book a security review.
Custom pricing for 100+ seats. Multi-year commits and rollout services available. Pilot in parallel with paper while contracts close.
CIO & procurement FAQ
FAQ
What's the SSO and SCIM story? (coming soon)
Google and Microsoft SSO are in development and next on the published roadmap, followed by Okta, Azure AD, and SAML 2.0. SCIM 2.0 provisioning ships with the SAML release - auto-onboard the day someone starts in your IdP, auto-revoke the day they leave. Today, CSV-driven bulk provisioning covers onboarding and offboarding.
Is HeyDrop SOC 2 certified?
SOC 2 Type II is on our published security roadmap. Today we operate to SOC 2 controls (encryption in transit and at rest, scoped access, vendor management, incident response). We can share our security questionnaire and ISO 27001-aligned controls map under NDA. See the Trust Center for what's live today vs. roadmap.
Where is data hosted and what's the data-residency story?
Hosted in encrypted US data centers (AWS us-east-1 / us-west-2). GDPR compliance is covered by our DPA with EU Standard Contractual Clauses, and AWS is certified under the EU-US Data Privacy Framework for lawful international transfers. Subprocessors list published at /security/subprocessors and updated under change-control.
Can we use our own domain - cards.acme.com?
Yes. Custom domain (e.g. cards.acme.com) is included on Enterprise plans. SSL provisioned, traffic routed, brand intact end-to-end. The recipient experience is yours, not heydrop.app.
What's the audit log story for compliance reviews? (coming soon)
Audit logging ships with the enterprise security release on our published roadmap, alongside SSO. Today, admin actions are tracked internally and account activity reports are available on request - auditors get a CSV, not a screenshot.
Do we get a dedicated Customer Success Manager? (coming soon)
A named CSM with quarterly business reviews is coming to Enterprise plans. Today, every Enterprise rollout gets white-glove onboarding - rollout plan, brand template setup, training for admins and end-users - plus a direct escalation channel to the founding team.
What's the DPA and contracting process?
Standard DPA available at /security/dpa with EU SCCs included. Master Services Agreement available for negotiation; we accommodate enterprise legal review. Typical signature cycle: 2-4 weeks depending on your contracting team. Pilot can start in parallel with paper.
What's pricing for an enterprise rollout?
Custom - based on seat count, contracting depth, and rollout services scope. As a reference: 500 seats lands well below comparable enterprise platforms; 5,000+ seats benefits from volume pricing. Multi-year commitments unlock further discount. Talk to sales.